

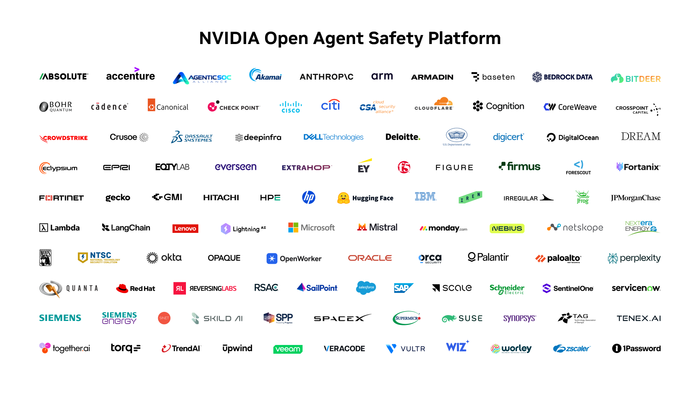
The Open Secure AI Alliance, now comprising over 120 organizations, is formulating new guidelines to bolster cybersecurity for agentic AI as the Black Hat conference commences in Las Vegas. The Linux Foundation has released a Request for Comments on the Shared AI Findings Exchange (SAFE), aimed at transforming cybersecurity incidents into collective protection for the AI ecosystem.
These SAFE guidelines propose the confidential collection and analysis of AI-related incidents, informing affected parties, identifying recurring failures, and publishing evidence-based recommendations to mitigate systemic risks. The initiative emphasizes the importance of shared threat intelligence among trusted ecosystems to enhance collective defense against evolving cyber threats.
As the SAFE framework progresses, it will complement the technological advancements made by Open Secure AI Alliance members, including NVIDIA, Cisco, and CrowdStrike. The focus will be on creating open, inspectable tools across the AI security stack, with an emphasis on community collaboration to address complex security challenges effectively. No further timeline was disclosed at the time of publication.
Editor's Note
The development of the SAFE guidelines reflects a growing recognition of the need for robust cybersecurity measures in the rapidly evolving AI landscape. As organizations increasingly rely on AI technologies, the collaborative approach advocated by the Open Secure AI Alliance could significantly enhance the resilience of AI systems against cyber threats. Stakeholders should monitor the implementation of these guidelines and their impact on industry practices.













Leave a comment