

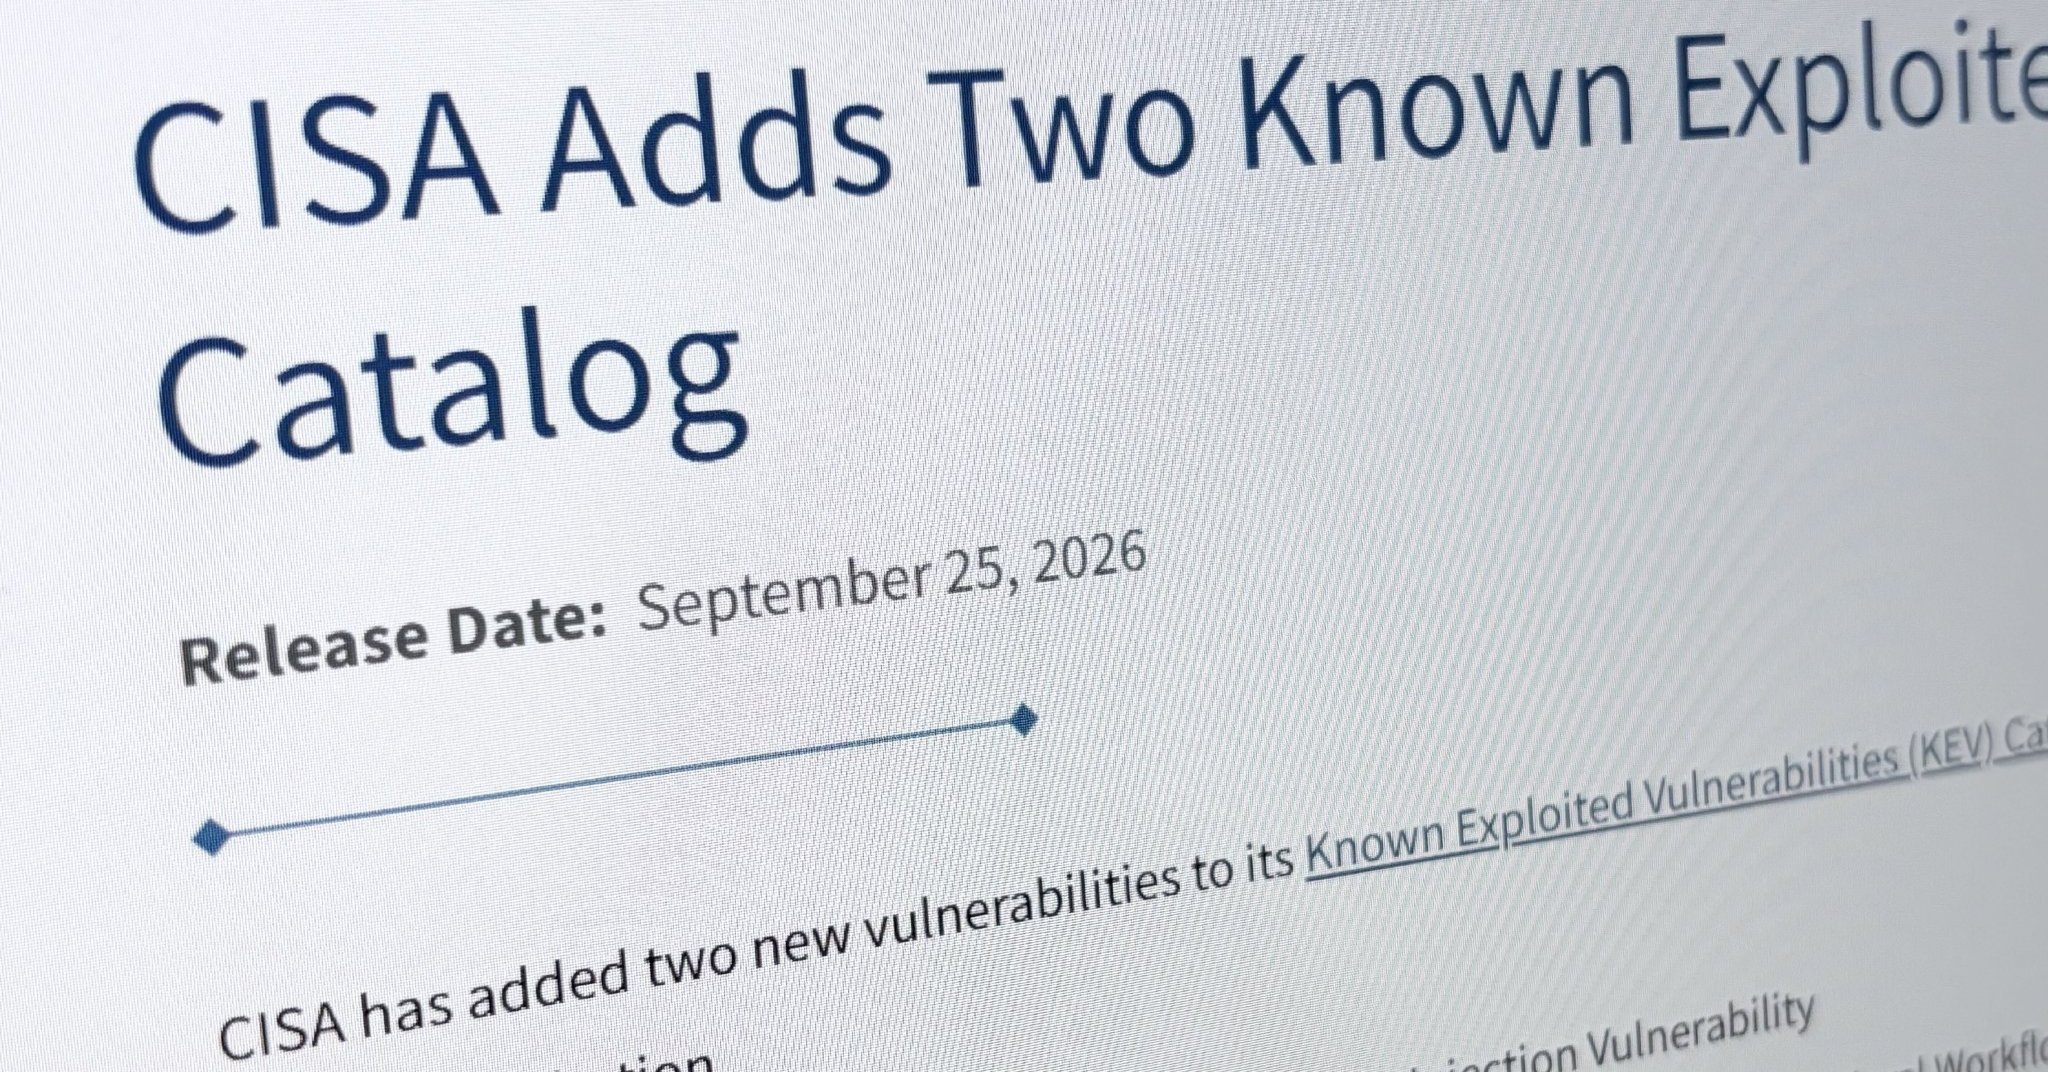
On September 25, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a vulnerability in Microsoft's SharePoint Server to its Known Exploited Vulnerabilities (KEV) list, indicating it is being actively exploited in cyber attacks. The vulnerability, identified as CVE-2026-65660, allows attackers to execute unauthorized programs on the server by sending crafted requests after logging into SharePoint.
This vulnerability poses significant risks, particularly for environments that have not adequately applied past security updates. According to Canadian cybersecurity authorities, servers that permit anonymous access can be exploited in conjunction with other SharePoint vulnerabilities to run unauthorized programs without authentication. CISA warns that such vulnerabilities are frequently targeted as entry points for cyber attacks, posing serious risks to U.S. federal systems and all organizations, including businesses.
Microsoft has urged users to apply all relevant updates for affected versions of SharePoint, including SharePoint Enterprise Server 2016, SharePoint Server 2019, and SharePoint Server Subscription Edition. No further timeline was disclosed at the time of publication.
Editor's Note
The identification of CVE-2026-65660 highlights the ongoing challenges organizations face in maintaining cybersecurity. With the increasing sophistication of cyber threats, it is crucial for enterprises to prioritize the application of security updates and to monitor for vulnerabilities listed in the KEV. This incident underscores the importance of proactive cybersecurity measures in safeguarding sensitive information and infrastructure.












Leave a comment