

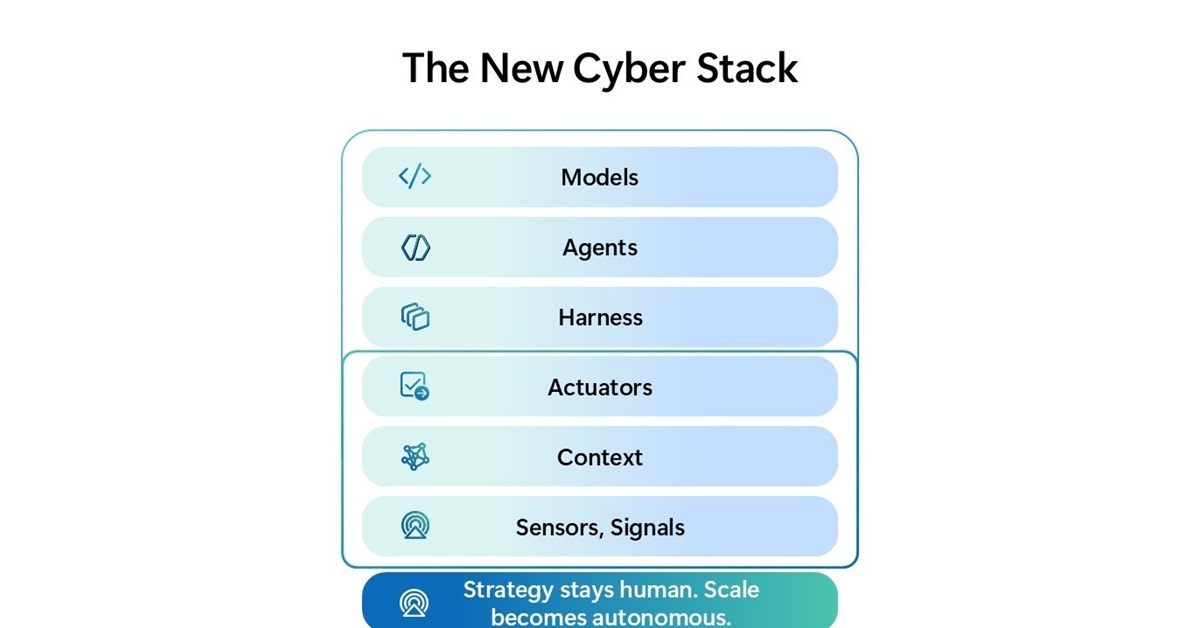
On September 23, 2026, Microsoft began offering a preview of the Integrated Security Operations Center (ISOC) within Microsoft Defender. This platform integrates SIEM, XDR, threat intelligence, automation, and AI capabilities, enabling security personnel and AI agents to collaborate effectively in a unified environment.
The introduction of ISOC is significant as it addresses the evolving threat landscape where attackers increasingly leverage AI to execute complex attacks independently. By transitioning from traditional security frameworks to an integrated model, Microsoft aims to enhance defensive capabilities and streamline operations for security teams.
Looking ahead, Microsoft has outlined that the ISOC preview is available to customers with specific licenses, including Microsoft Defender Suite and Microsoft 365 E5 and E7. Organizations without an active Microsoft Sentinel workspace can participate, while existing Sentinel users are advised to maintain their current environments. No further timeline was disclosed at the time of publication.
Editor's Note
The launch of Microsoft's ISOC marks a pivotal shift in security operations, emphasizing the need for integrated solutions in response to advanced cyber threats. As organizations increasingly face sophisticated attacks, the adoption of such technologies will be crucial for maintaining robust security postures and operational efficiency.











Leave a comment